Data Breach Overview
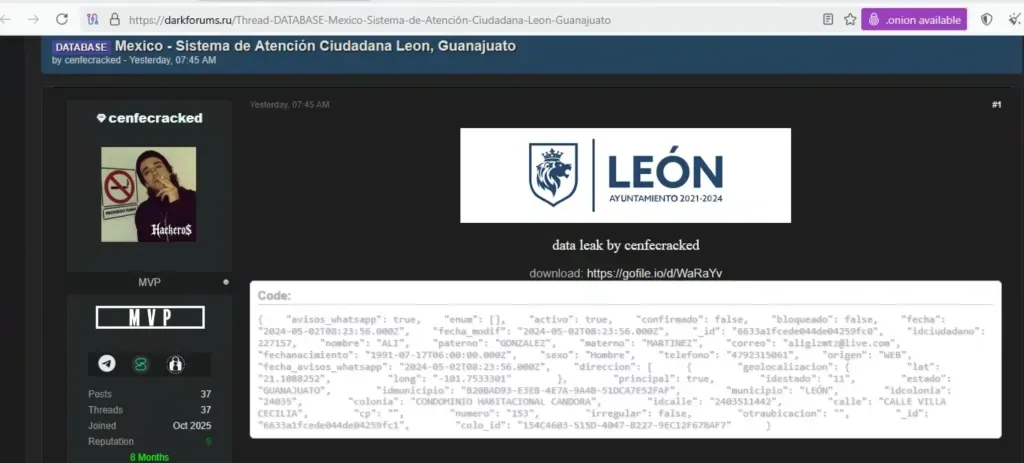
A threat actor using the alias cenfecracked has claimed to leak data from the Sistema de Atención Ciudadana (SAC) operated by the Municipality of León, Guanajuato, Mexico. The uploaded screenshot shows a forum post advertising a downloadable database and displaying sample records in JSON format.
Public reporting indicates the leaked file may be named SACleonguanajuato.json, reportedly larger than 200 MB, and could affect approximately 250,000 citizens. Reported exposed fields include names, phone numbers, email addresses, home addresses, CURP data, and precise geographic coordinates.
Where Was the Data Found?
The data was shown circulating on a dark web/criminal forum, where the actor posted a download link and a sample of the alleged records. The sample visible in the screenshot includes personal identifiers, contact details, address-related fields, and geolocation information.
The Municipality of León has reportedly filed a criminal complaint with the Guanajuato State Prosecutor’s Office and stated that the SAC is used by residents to submit municipal service reports and requests, including potholes, street-light failures, water leaks, and similar issues.
Company Data Breach History
Public sources show that this is not the first recent cybersecurity incident involving León’s municipal systems. Reports from June 2026 described a separate incident involving the city’s emergency/911-related systems, allegedly exposing 178,793 prehospital care records containing personal and medical information.
No older confirmed SAC-specific breach was found in the quick search, but León and Guanajuato public-sector systems have been mentioned in several recent cyber incident reports.
Impact and Risks
The exposed information could create serious risks for affected residents. Attackers may use the data for phishing, identity theft, fraud, extortion, harassment, doxxing, or targeted scams. The presence of addresses and geolocation data increases the risk of physical-world targeting, especially if combined with other leaked records.
Recommendations for Users
Affected users should change passwords on any accounts that reuse similar personal details, enable two-factor authentication, and avoid using the same password across multiple services. They should also monitor bank, email, and government-service accounts for unusual activity, be cautious of calls or messages referencing municipal reports, and report suspicious contact to the relevant authorities.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.