Data Breach News2 min read
U.S. Area 51 Documents Exposed in Claimed 18GB Leak
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Overview
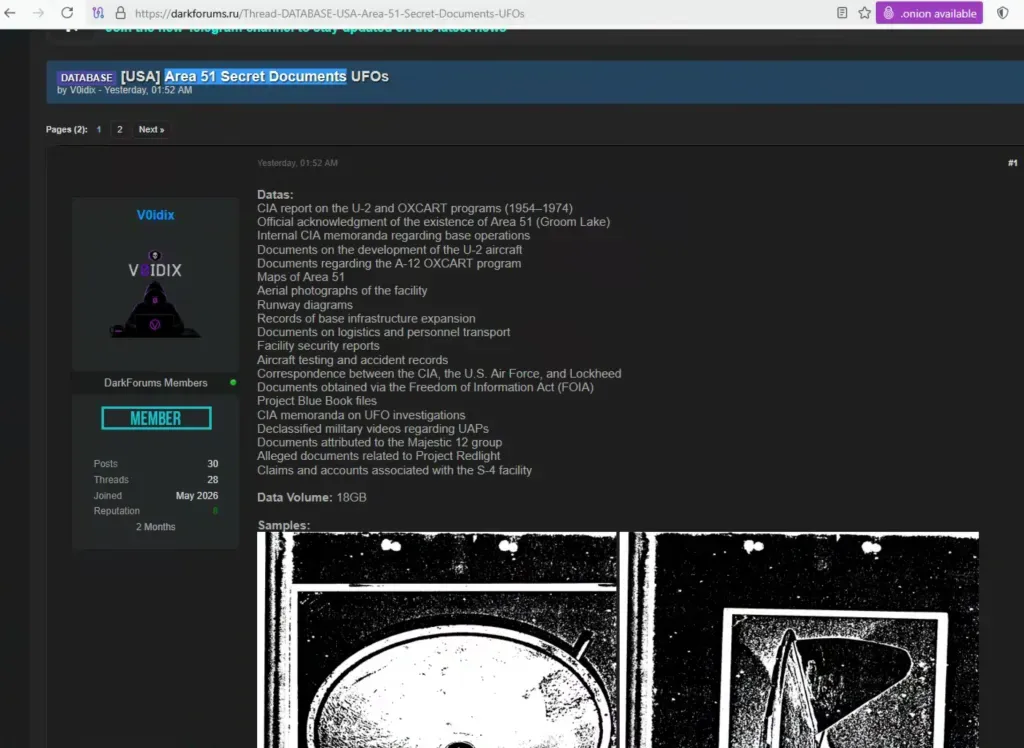
In late July 2026, a forum user operating under the name V0idix claimed to have released an 18GB archive of U.S. government documents connected to Area 51, the CIA, and the U.S. Air Force.
The material was advertised as containing records about the U-2 and A-12 OXCART reconnaissance programs, Groom Lake operations, aircraft testing, security procedures, UFO investigations, and other historically sensitive subjects. The forum listing confirms the existence of the thread, but the archive’s origin and authenticity remain unverified.
Where Was the Data Found?
The archive was posted in the database section of DarkForums, a forum commonly used to distribute leaked and republished datasets.
According to the author, the 18GB collection includes:
- CIA reports and internal memoranda
- U-2 and A-12 OXCART development records
- Area 51 maps, aerial photographs, and runway diagrams
- Infrastructure, logistics, and personnel-transport documents
- Facility security reports
- Aircraft testing and accident records
- Correspondence involving the CIA, U.S. Air Force, and Lockheed
- Project Blue Book and UFO investigation files
- Declassified military videos involving UAPs
- Documents attributed to Majestic 12
- Alleged Project Redlight and S-4 material
Impact and Risks
The severity of this incident depends on whether the archive contains genuinely new and restricted information.
Authentic operational or personnel records could expose historical security procedures, identify individuals, support targeted social-engineering campaigns, or reveal information that was not intended for public distribution. A mixture of genuine records and fabricated material could also be used to spread misinformation.
Anyone obtaining copies from an untrusted forum faces an additional risk of malware, credential-stealing software, or malicious files disguised as government documents.
Recommendations
Avoid downloading or opening the archive from unofficial sources. Researchers handling a copy should use an isolated analysis environment and verify documents against official CIA, FBI, and National Archives collections.
Anyone who registered on the forum, entered credentials, or downloaded executable content should change affected passwords immediately, enable two-factor authentication, use unique credentials, scan their device, and monitor accounts for suspicious activity.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.