Data Breach News2 min read
OVP Software SQL Database Allegedly Exposed
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Overview
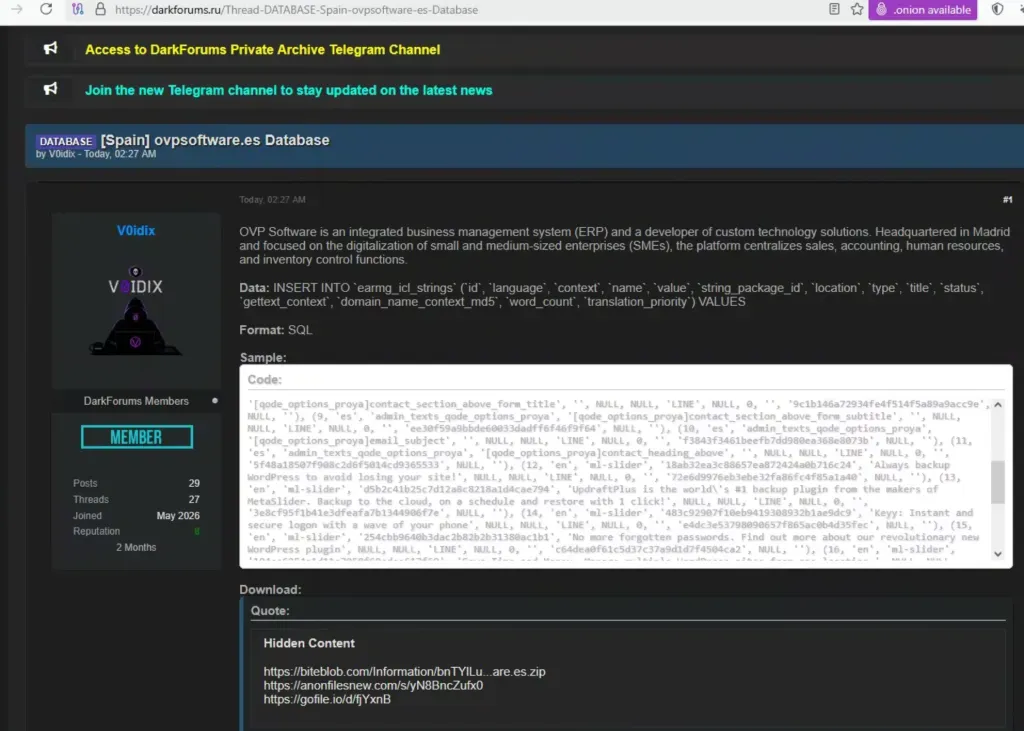
In July 2026, a threat actor using the alias V0idix allegedly published data associated with OVP Software on the cybercrime forum DarkForums.
OVP Software is a Spanish technology provider offering ERP, CRM, billing, e-commerce, and other business-management solutions.
The exposed material was distributed in SQL format. The total database size and number of affected records were not disclosed.
Where Was the Data Found?
The database was reportedly shared on darkforums.st, an underground forum used to distribute leaked databases, malware, hacking tools, and other cybercrime-related material.
The provided sample contains an SQL INSERT statement for the earmg_icl_strings table. Its structure appears consistent with a WordPress multilingual translation or localization table and includes:
- Language codes
- Website configuration keys
- Translation strings
- Internal content identifiers
- MD5-style reference values
- Word counts and translation priorities
Company Data Breach History
A quick public-source review did not identify any earlier independently reported data breaches involving OVP Software.
Public threat-intelligence trackers have referenced the July 2026 DarkForums listing, but no official statement from OVP Software or independent confirmation of the database’s authenticity was located.
Impact and Risks
If the leaked material is limited to website translation strings and configuration data, the immediate risk to customers may be relatively low. Nevertheless, internal identifiers, plugin information, table structures, and configuration details could assist attackers with reconnaissance.
If additional database tables were included, the incident could potentially expose account information, business records, contact details, or administrative data.
Possible risks include:
- Targeted phishing and social-engineering attacks
- Identification of website technologies and plugins
- Exploitation of outdated WordPress components
- Unauthorized access attempts against related systems
- Fraudulent messages impersonating OVP Software
- Further compromise if credentials appear elsewhere in the archive
Recommendations for Users
OVP Software customers and users should:
- Change their passwords, particularly when credentials have been reused
- Enable two-factor authentication where available
- Use a unique password for every account
- Treat unexpected emails, invoices, and login links with caution
- Monitor business and financial accounts for suspicious activity
- Confirm security-related messages through official company channels
Website administrators should also review access logs, update WordPress and installed plugins, rotate database credentials, and determine whether any additional tables were accessed.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.