Data Breach Overview
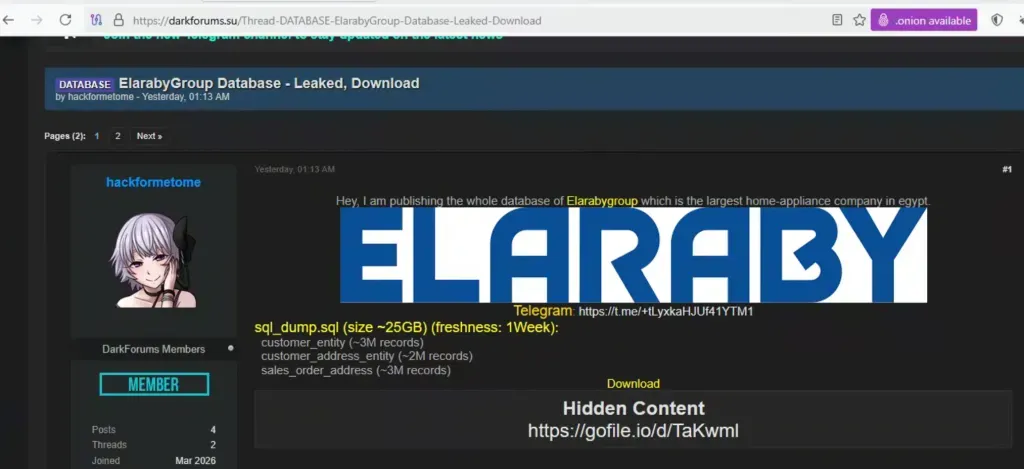
A threat actor using the alias “hackformetome” claims to have leaked the full database of Elaraby Group, one of Egypt’s major home appliance and consumer electronics companies. The alleged dump is listed as a 25GB SQL file and was described as being roughly one week fresh.
The exposed database reportedly includes several large tables, including:
- customer_entity — approximately 3 million records
- customer_address_entity — approximately 2 million records
- sales_order_address — approximately 3 million records
Elaraby Group is widely known in Egypt and operates across consumer electronics, home appliances, retail, sales, and after-sales services. Public company profile data describes it as a major regional business with more than 40,000 employees, thousands of sales partners, and hundreds of service centers.
Where Was the Data Found?
The alleged database was posted on a cybercrime forum and promoted with a Telegram contact. The post claimed the data was available for download through an external file-hosting service.
Based on the table names shown in the leak post, the exposed information may include customer account data, customer address records, and sales/order address details. This type of data can be highly useful for targeted scams, impersonation, and account-related fraud.
Company Data Breach History
A quick online search found recent reporting about the same alleged 25GB Elaraby Group database leak, including a June 2026 analysis describing exposed customer records, physical addresses, and transaction-related data.
There were also earlier public reports in 2024 claiming that ELARABY Group had been targeted by LockBit 3.0 ransomware. I did not find an official company statement confirming the full details of that earlier incident during this quick search.
Company Data Breach History
A quick online search found recent reporting about the same alleged 25GB Elaraby Group database leak, including a June 2026 analysis describing exposed customer records, physical addresses, and transaction-related data.
There were also earlier public reports in 2024 claiming that ELARABY Group had been targeted by LockBit 3.0 ransomware. I did not find an official company statement confirming the full details of that earlier incident during this quick search.
Impact and Risks
If the leaked data is authentic, affected customers may face increased risks of phishing, delivery scams, fake warranty or service-center messages, identity fraud, and social engineering attempts. Address and order-related information can also help attackers make fraudulent messages appear more convincing.
If any credentials, session data, or account identifiers are present in the broader dump, attackers may attempt account takeover, credential stuffing, or unauthorized access to related customer accounts.
Recommendations for Users
Customers who have used Elaraby Group’s online services should change their passwords immediately, especially if the same password was used on other websites. They should enable two-factor authentication where available, use unique passwords for every account, and watch for suspicious calls, emails, SMS messages, or WhatsApp messages claiming to be from Elaraby, delivery companies, warranty teams, or customer support.
Users should also monitor bank accounts and online shopping accounts for unusual activity and avoid clicking links sent through unexpected messages.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.