Data Breach News2 min read
Significant Data Breach at Orange Group
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
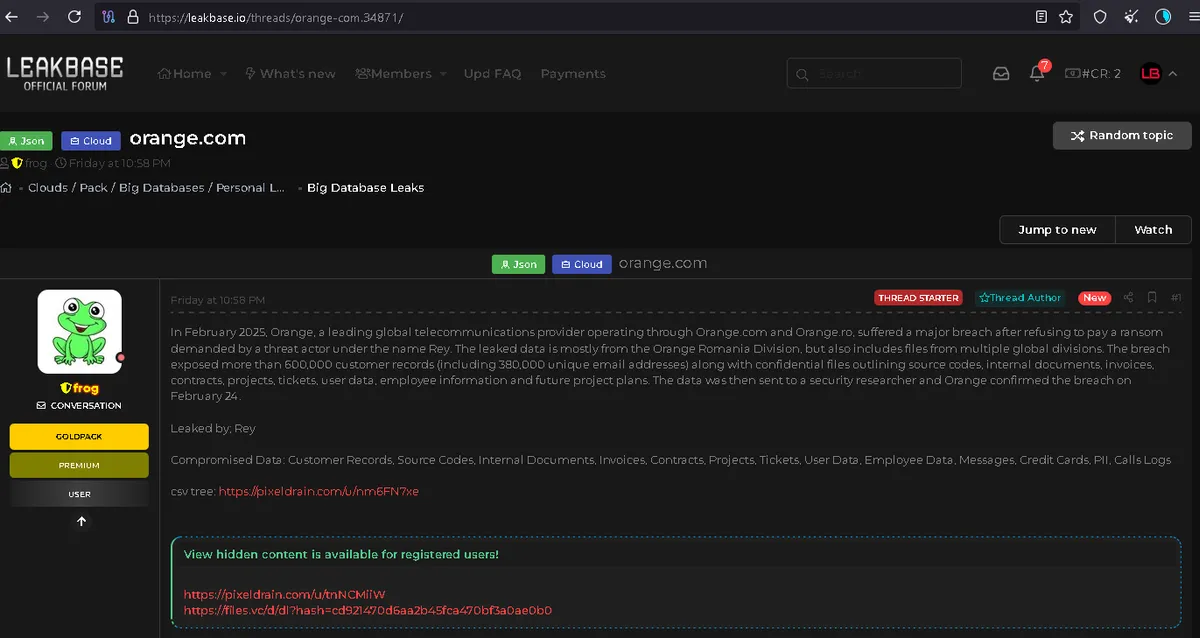
In February 2025, Orange Group, a leading global telecommunications provider operating through Orange.com and Orange.ro, experienced a significant data breach. The breach was orchestrated by a threat actor known as “Rey,” affiliated with the HellCat ransomware group. After Orange refused to pay the demanded ransom, Rey leaked approximately 6.5GB of sensitive data, primarily from the Orange Romania division, but also affecting multiple global divisions. The compromised data includes over 600,000 customer records, encompassing 380,000 unique email addresses, as well as internal documents such as source codes, invoices, contracts, projects, tickets, user data, employee information, and future project plans. Orange confirmed the breach on February 24, 2025.
Where and How?
The breach was discovered when the stolen data was leaked on the dark web forum leakbase.io by a user named “frog.” The threat actor, Rey, claimed to have maintained access to Orange’s systems for over a month by exploiting compromised credentials and vulnerabilities in the company’s Jira software and internal portals. The data exfiltration occurred over a three-hour period without detection. The leaked data includes email addresses of current and former Orange Romania employees, partners, and contractors, along with partial payment card details of Romanian customers, some of which were expired. Additionally, customer records from Yoxo, Orange’s contract-free subscription service, were part of the breach.
Company Data Breach History
Prior to this incident, there were no widely reported data breaches involving Orange Group’s Romanian division. However, this breach underscores potential vulnerabilities within the company’s security protocols, indicating a need for more robust measures to prevent future incidents. Orange has stated that the breach occurred on a non-critical back-office application and that there was no impact on customer operations. The company has initiated an investigation and is cooperating with relevant authorities to assess the breach’s scope and mitigate its impact.
Recommendations for Personal Data Protection
How Users Can Protect Their Information
To safeguard personal information and accounts, users should consider the following steps:
- Change Passwords Regularly: Use strong, unique passwords combining letters, numbers, and symbols.
- Enable Two-Factor Authentication (2FA): Whenever possible, activate 2FA to add an extra layer of security to accounts.
- Use Unique Passwords for Each Account: Avoid reusing passwords across different platforms to prevent multiple account compromises.
- Be Cautious of Phishing Attempts: Stay vigilant against suspicious emails or messages that may contain malicious links or solicit personal information.
- Monitor Accounts for Unusual Activity: Regularly review account statements and activities to detect and respond promptly to unauthorized actions.
By adopting these practices, users can enhance their personal data security and reduce the risk of unauthorized access to their information.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.