Data Breach News2 min read
Medstartr.com Database
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
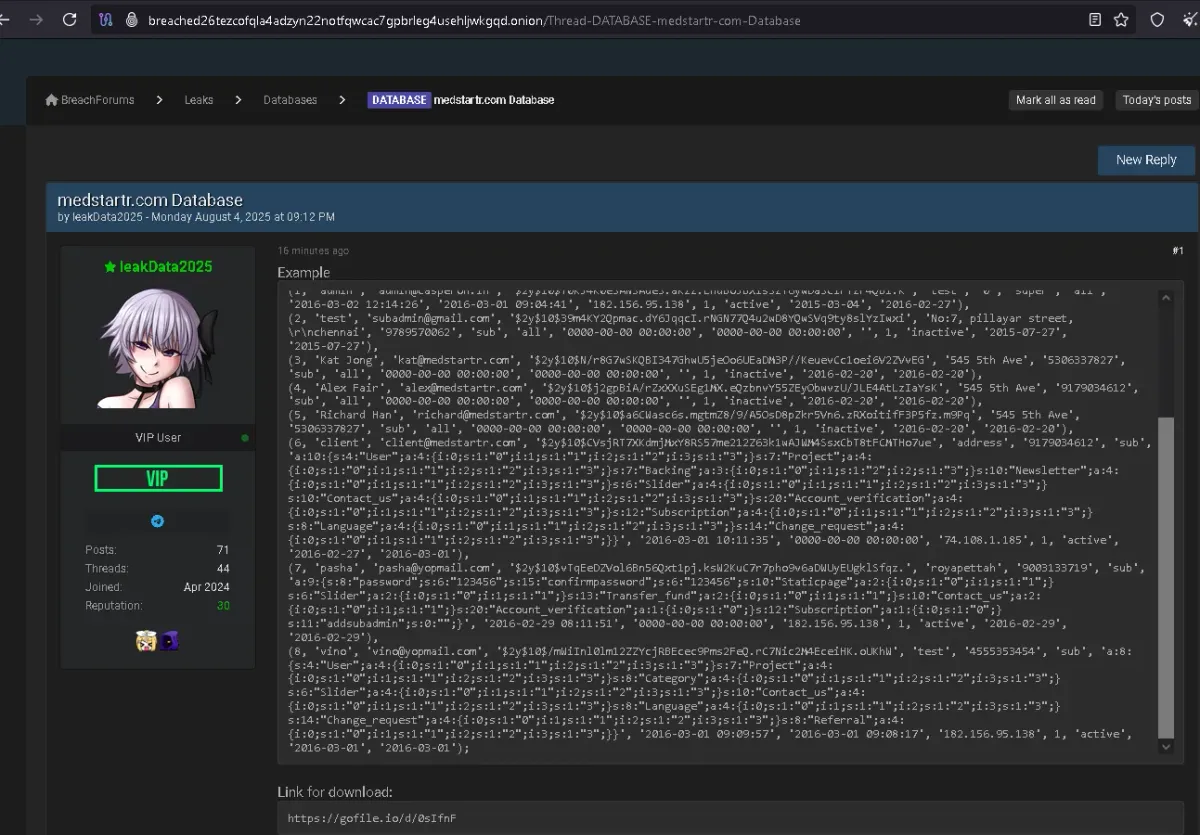
In August 2025, a user identified as leakData2025 published a database allegedly belonging to medstartr.com on BreachForums. The leak contains a SQL dump with administrative and user-level data including emails, hashed passwords, physical addresses, login IPs, timestamps, and account roles.
The data includes full entries like administrator accounts (admin@casperon.in, subadmin@gmail.com) with hashed credentials using bcrypt, along with verification status, user activity logs, and privilege levels. While some entries date back as far as 2015, the exposure of privileged account data remains a serious threat for exploitation.
Where and How?
The breach appeared on the cybercrime marketplace BreachForums, where the attacker posted an SQL export from the medstartr.com system. The database contains detailed information on system users, administrators, login patterns, and privileges—making it especially dangerous for spear-phishing and targeted attacks.
The leak demonstrates how legacy data, even from as far back as 2015, continues to pose risks when not properly secured or decommissioned. Hashes may resist immediate cracking, but the visibility of user structures and admin roles significantly elevates the threat level.
Company Data Breach History
No previously reported data breaches associated with medstartr.com were found in public sources. This marks the first known incident involving the exposure of internal administrative data. The scope and sensitivity of the leaked database highlight a pressing need for the company to assess long-term data retention practices and apply modern security protocols retroactively.
Recommendations for Personal Data Protection
To protect themselves, users are advised to:
- Immediately change any reused passwords.
- Enable two-factor authentication (2FA).
- Use unique passwords for each service.
- Be vigilant against suspicious messages or phishing attempts.
- Monitor related accounts for unusual activity.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.