Data Breach News2 min read
SQL Dump Leak Exposes User Data from lamundialdeseguros.com
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
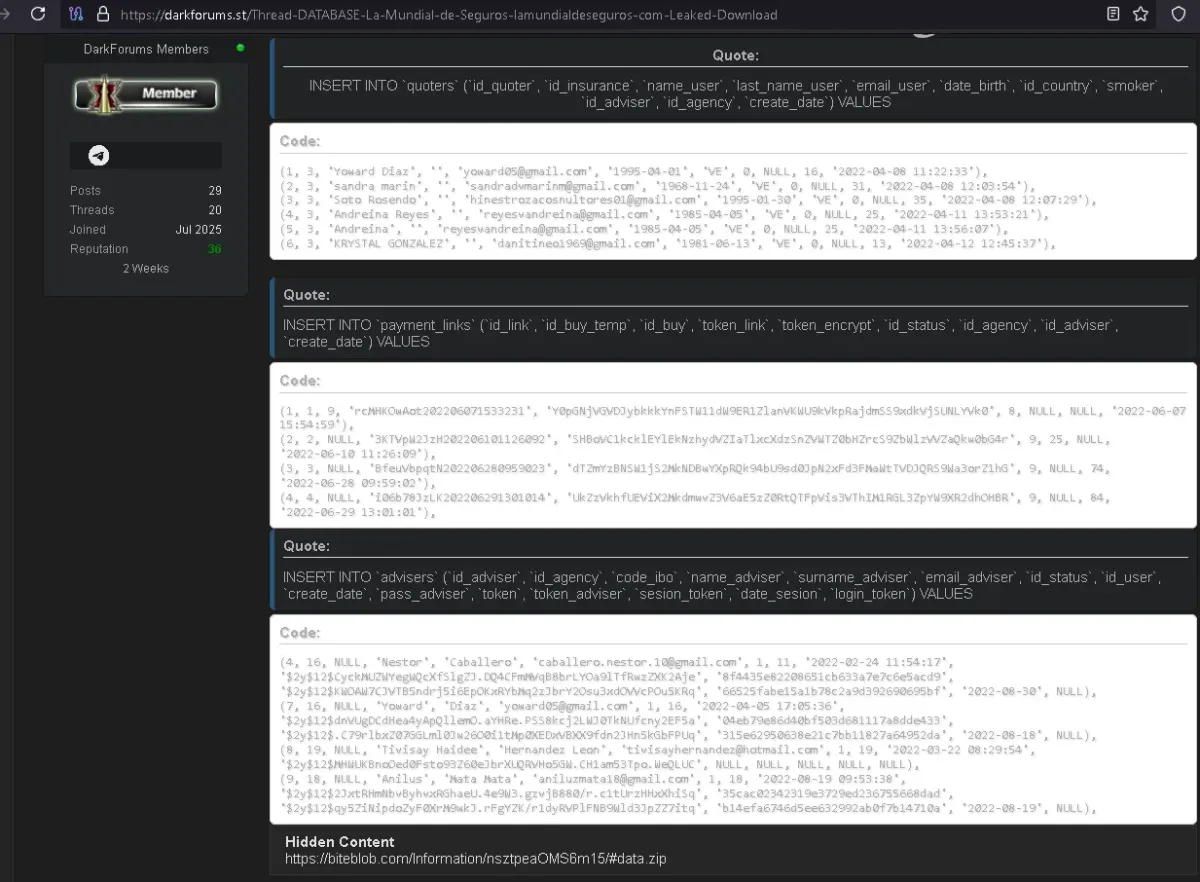
A new data leak has surfaced involving the database of lamundialdeseguros.com, with sensitive information being published on darkforums.st in August 2025 by the user N1KA. The leaked content consists of raw SQL insert statements, exposing user data, adviser credentials, and payment link details. This breach highlights the exposure of personally identifiable information (PII), including full names, email addresses, birthdates, hashed passwords, tokens, and more.
The leak provides direct insight into the backend structure of the company’s quoting and adviser system, raising concerns over insufficient data protection measures within the insurance platform.
Where and How?
The breach was found on darkforums.st, where the attacker N1KA posted several SQL insert statements from lamundialdeseguros.com’s backend database. These include tables such as quoters, advisers, and payment_links, each containing sensitive client and internal user data.
Notably, adviser accounts were leaked with encrypted passwords and session tokens, while customer quote records revealed full names, emails, and birthdates — all potentially useful for identity theft or phishing attacks. The inclusion of payment_links further suggests access to transactional or billing systems.
The nature of the exposed data implies a compromise of the company’s internal systems or databases, with the dump suggesting either a misconfigured server or a direct database exfiltration.
Company Data Breach History
According to public sources, lamundialdeseguros.com was previously targeted in December 2024 by the ransomware group Funksec, as reported by BreachSense. While that incident was ransomware-related, the current leak appears to be a separate event originating from unauthorized data access and exfiltration rather than encryption/extortion tactics.
These repeated breaches underline serious weaknesses in the organization’s cybersecurity posture, particularly in database security and access control.
Further Action:
The affected organization should promptly investigate the origin of the breach, reinforce data protection policies, and notify users whose data may have been exposed. Immediate security audits and better access control mechanisms are strongly recommended.
Recommendations for Personal Data Protection
How Users Can Protect Their Information
To protect their personal information and accounts from being compromised, users should take the following steps:
- Change their passwords frequently, with a combination of letters, numbers, and symbols.
- Enable two-factor authentication whenever possible.
- Use unique passwords for each account to prevent attackers from gaining access across platforms.
- Be cautious of suspicious emails or messages, especially those containing links or attachments.
- Regularly monitor financial and digital accounts for any suspicious activity.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.