Data Breach News3 min read
Doctor Alliance, LLC Sensitive Data Breach
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Overview
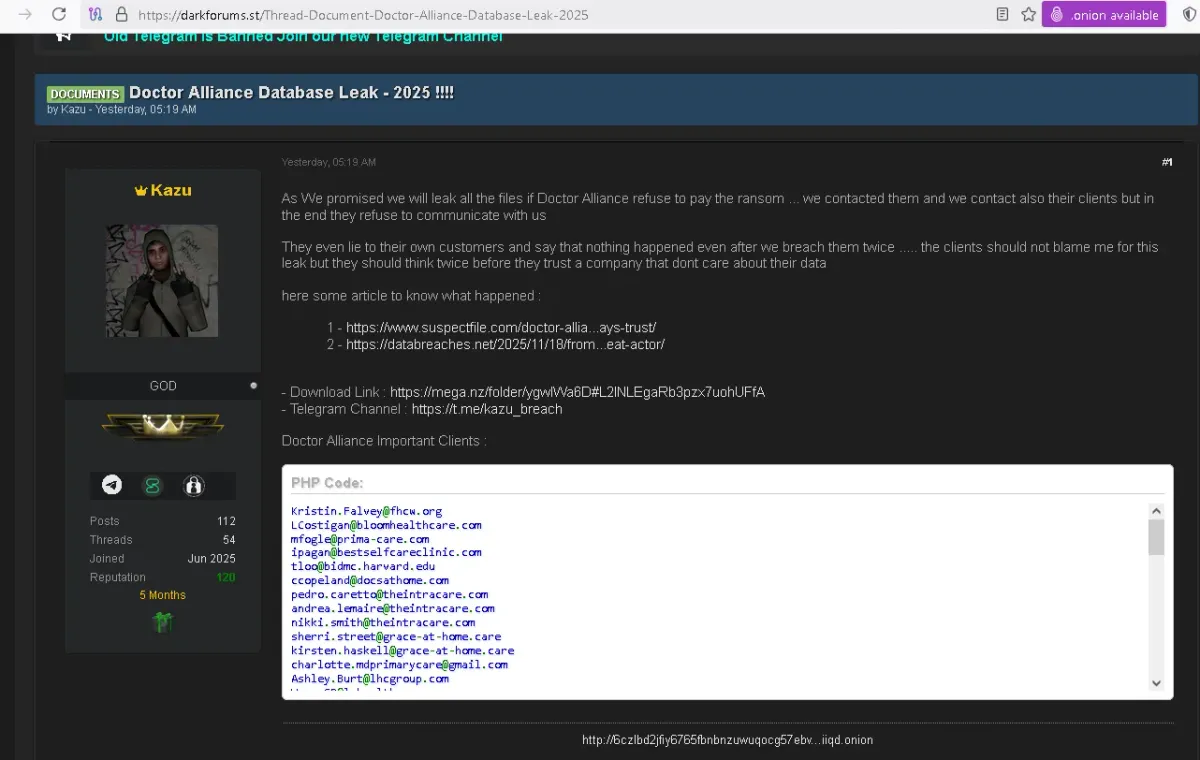
On November 2025, an actor identified as “Kazu” posted on dark‑forum channel (apparently darkforums.st) that they had breached the systems of Doctor Alliance. The actor claims that, after a ransom demand was refused, they will leak the company’s files. According to the claim, the data includes millions of files belonging to the company and its clients.
The actor states they attempted to contact Doctor Alliance and its clients; when communication failed, they began the leak. They accuse the company of telling customers nothing happened, despite two separate intrusions.
Where Was the Data Found?
The actor posted a download link (https://mega.nz/folder/ygwlWa6D#L2INLEgaRb3pzx7uohUFfA) and runs a Telegram channel (t.me/kazu_breach) where the data is purportedly shared.
They also list a set of clients / email addresses allegedly impacted by the breach (including Kristin Falvey@fhcw.org
Company Data Breach History
According to public reporting:
- Doctor Alliance is a U.S.‑based healthcare technology vendor providing billing, document management and EHR‑adjacent services.
- On or around November 7, 2025, the hacker claimed to have stolen approximately 353 GB of data, over 1.24 million files.
- Reports indicate the actor demanded about USD 200,000 ransom, with a deadline of November 21, 2025, to delete the data.
- Some commentary claims a second breach occurred, possibly of ~1.27 TB of data, though that remains unverified.
- The company has not publicly confirmed full details of the breach; they acknowledged unauthorized access to “a single client account” and said they are investigating.
Impact & Risks
The data reportedly includes names, addresses, phone numbers, email addresses, Medicare and medical record numbers, diagnoses, treatment plans, medications and dosages, and provider information.
Potential risks include:
- Identity theft: Attackers may use personal information for fraud or to open accounts in victims’ names.
- Medical identity theft: Using stolen PHI to file fraudulent claims, obtain prescriptions, or impersonate patients.
- Targeted phishing or extortion: With detailed medical histories, attackers can craft convincing attacks or blackmail individuals.
- Regulatory and reputational damage: Given the HIPAA obligations of a business‑associate in the U.S., there may be regulatory fines, lawsuits and loss of trust.
- Long‑term exposure: Unlike a password which can be changed, medical histories cannot. Once exposed, the damage may be permanent.
Recommendations for Affected Individuals
If you suspect you may be impacted, consider:
- Changing passwords to any associated accounts, especially healthcare portals, email accounts, etc.
- Enabling multi‑factor authentication (MFA/2FA) where available.
- Monitoring your healthcare records and insurance statements for unfamiliar claims or treatments.
- Freezing or placing fraud alerts on your credit reports if relevant.
- Considering identity theft protection services (though note these may not mitigate all risks of PHI misuse).
- Contacting the entity (Doctor Alliance) or their clients to ask if you’ve been notified as affected.
- Being alert to phishing attempts or unsolicited contact posing as healthcare providers, insurers, or the vendor.
- Keeping records of any suspicious activity or correspondence relating to your healthcare or identity.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.