Data Breach News2 min read
43 GB Database Breach — Streebo Hit by Everest ransomware group
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Overview
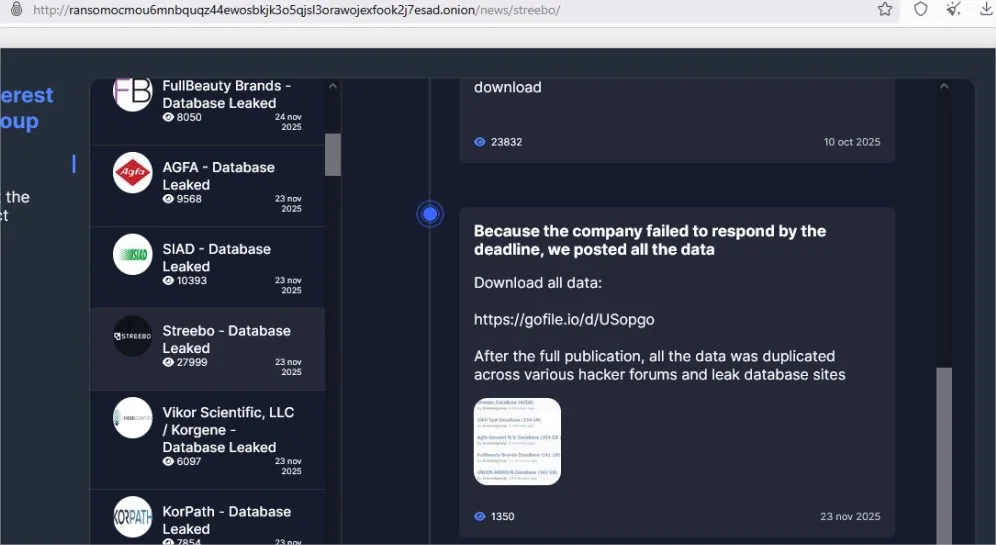
According to recent reports, a database of approximately 42–43 GB belonging to Streebo (streebo.com) was allegedly leaked online. The leak is attributed to the ransomware group Everest, following an attack discovered in October 2025.
Where Was the Data Found?
The data dump reportedly surfaced on a hacker forum — a common type of darknet site used by threat actors to publish stolen files.
The exposed material is described as a “database,” which suggests it could include proprietary files, internal records, perhaps source code, client info, or other sensitive assets.
Company Data Breach History
- There is no publicly documented prior incident involving Streebo, indicating this may be their first known data breach.
- However, the Everest ransomware group has a history of high‑profile attacks: since 2020 the group has targeted multiple organizations, often leaking databases, internal files, or sensitive company/customer data.
Impact and Risks
- If legitimate, the leak may expose sensitive corporate data — potentially including intellectual property, internal communications, and client or employee records.
- Such data could be abused for corporate espionage, fraud, social engineering attacks, or the creation of forged credentials.
- The leak may also damage Streebo’s reputation and erode trust among clients, partners, and stakeholders.
Recommendations for Users & Stakeholders
- If you are a Streebo client, partner, or employee: review any credentials or access permissions you have related to Streebo services and assume they may be compromised.
- Consider changing passwords and enforcing strong, unique credentials — especially where you used the same password elsewhere.
- If you manage or use systems tied to Streebo, enable or enforce multi‑factor authentication (MFA/2FA) wherever possible.
- Monitor for any suspicious communications or activity (unauthorized access attempts, phishing emails, unusual requests) that might leverage leaked data.
- For companies working with third‑party vendors: treat this incident as a reminder to audit vendor security practices, enforce strict access controls, and ensure contractual obligations for data protection.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.