Data Breach News2 min read
19GB of Data from Gloria Cales Leaked on Dark Web Forum “MONTI”
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
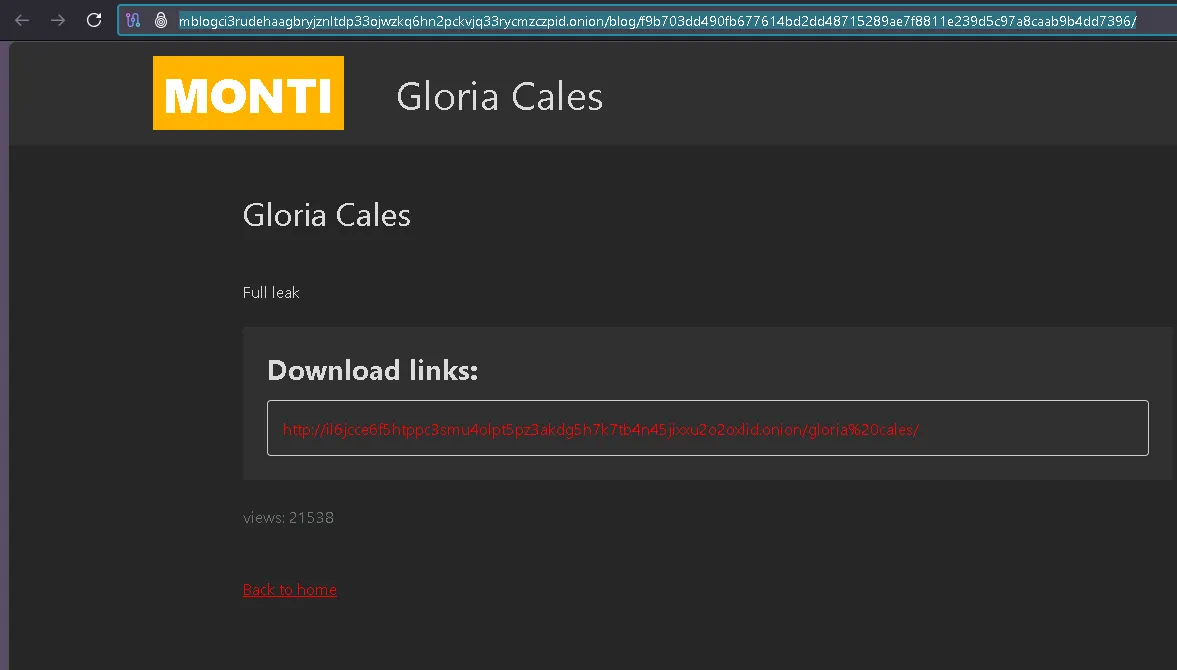
On March 19, 2025, InsecureWeb identified a breach involving Gloria Cales, with approximately 19GB of internal corporate data leaked on the dark web forum MONTI. The attack was confirmed on platforms such as RansomLook and Aarvicom CyberWatch, where Gloria Cales was listed as a “full leak” victim by the MONTI ransomware group.
This breach indicates that threat actors were able to infiltrate company systems and extract sensitive information, which was then made publicly accessible on underground forums.
Where and How?
The leak was published on MONTI, a dark web site operated by a ransomware group of the same name. The exposed data reportedly includes various internal files and potentially confidential documentation, though specific content details remain limited. The fact that the leak was classified as a “full leak” suggests that Gloria Cales may have refused to comply with ransom demands, leading the attackers to publish the stolen data in retaliation.
As of now, there is no confirmation of customer data being affected, but internal corporate operations could be heavily impacted.
Company Data Breach History
There are no previously reported breaches involving Gloria Cales prior to this event. However, this incident brings to light serious security flaws that may have gone unnoticed. The presence of the company’s name on ransomware tracking databases suggests that they were directly targeted by cybercriminals looking to extort or publicly damage the organization.
Further Action
InsecureWeb urges Gloria Cales to take immediate action:
- Launch a detailed forensic investigation to determine the extent of the breach.
- Inform affected parties and comply with GDPR or other regulatory obligations.
- Patch vulnerabilities used by attackers and rotate all compromised credentials.
- Collaborate with law enforcement and cybersecurity experts to understand and prevent future attacks.
- Communicate openly with stakeholders about the incident and mitigation steps.
Recommendations for Personal Data Protection
How Users Can Protect Their Information
To safeguard personal information and accounts, users should consider the following steps:
- Change Passwords Regularly: Use strong, unique passwords combining letters, numbers, and symbols.
- Enable Two-Factor Authentication (2FA): Whenever possible, activate 2FA to add an extra layer of security to accounts.
- Use Unique Passwords for Each Account: Avoid reusing passwords across different platforms to prevent multiple account compromises.
- Be Cautious of Phishing Attempts: Stay vigilant against suspicious emails or messages that may contain malicious links or solicit personal information.
- Monitor Accounts for Unusual Activity: Regularly review account statements and activities to detect and respond promptly to unauthorized actions.
By adopting these practices, users can enhance their personal data security and reduce the risk of unauthorized access to their information.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.