Data Breach News2 min read
16GB Leaked from Omni Fiber LLC After Monti Ransomware Attack
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
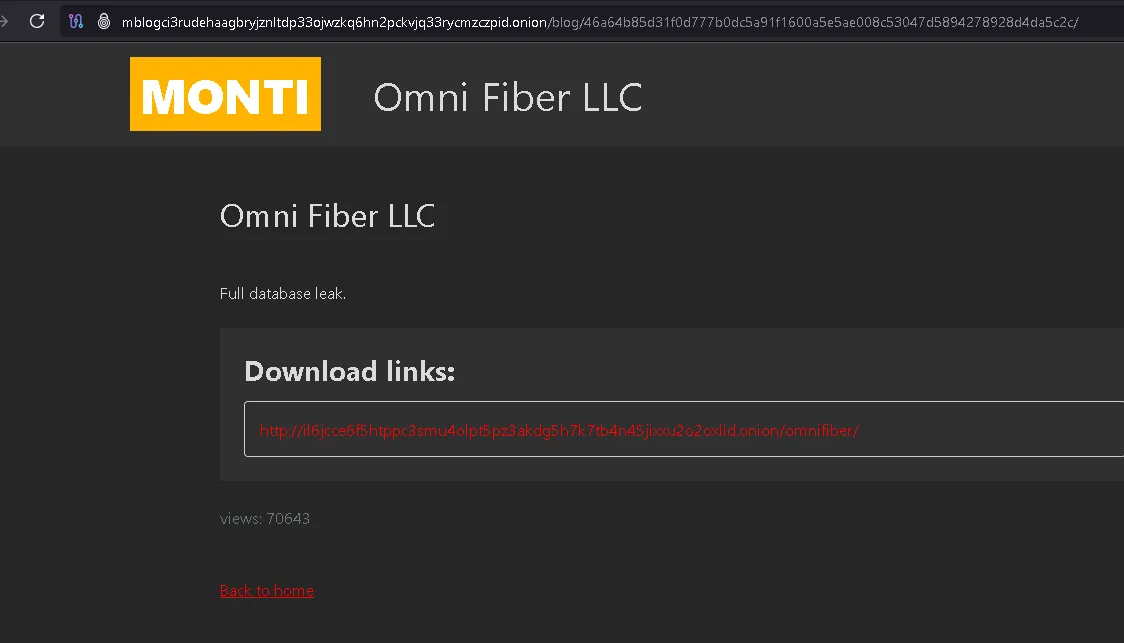
On February 12, 2025, telecommunications provider Omni Fiber LLC was hit by a ransomware attack carried out by the Monti hacker group. The breach resulted in the leak of 16GB of sensitive customer data. This compromised information may include personal and potentially financial details, emphasizing the urgent need for stronger cybersecurity measures. The incident was later confirmed after data was found circulating in dark web forums and leak sites monitored by cybersecurity researchers.
Where and How?
The breach was executed by the Monti ransomware gang, known for targeting telecom and infrastructure-related companies. Following the attack, the stolen data was published across underground platforms and messaging services, making it accessible to malicious actors. The exposure of such a large data set highlights critical vulnerabilities in Omni Fiber LLC’s cloud and internal security systems. This incident serves as a reminder of the increasing sophistication of ransomware groups and the ease with which they can exfiltrate and publish sensitive company data.
Company Data Breach History
Prior to this incident, there were no publicly known or reported data breaches involving Omni Fiber LLC. However, the recent attack suggests gaps in their existing security protocols, and it raises concerns about the company’s preparedness to defend against future threats. The breach has likely caused significant reputational damage and places added pressure on Omni Fiber LLC to reassess and upgrade its cybersecurity infrastructure.
Further Action
Omni Fiber LLC is strongly encouraged to:
- Conduct a full forensic investigation to determine the breach’s origin.
- Immediately implement enhanced security policies, including data encryption and better access controls.
- Notify affected users and regulatory bodies in accordance with data protection laws.
- Be transparent with their user base about what was exposed and what is being done to prevent future incidents.
Recommendations for Personal Data Protection
How Users Can Protect Their Information
To safeguard personal information and accounts, users should consider the following steps:
- Change Passwords Regularly: Use strong, unique passwords combining letters, numbers, and symbols.
- Enable Two-Factor Authentication (2FA): Whenever possible, activate 2FA to add an extra layer of security to accounts.
- Use Unique Passwords for Each Account: Avoid reusing passwords across different platforms to prevent multiple account compromises.
- Be Cautious of Phishing Attempts: Stay vigilant against suspicious emails or messages that may contain malicious links or solicit personal information.
- Monitor Accounts for Unusual Activity: Regularly review account statements and activities to detect and respond promptly to unauthorized actions.
By adopting these practices, users can enhance their personal data security and reduce the risk of unauthorized access to their information.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.