Data Breach News2 min read
Zebra Technologies Source Code Breach Exposes Internal Files
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Overview
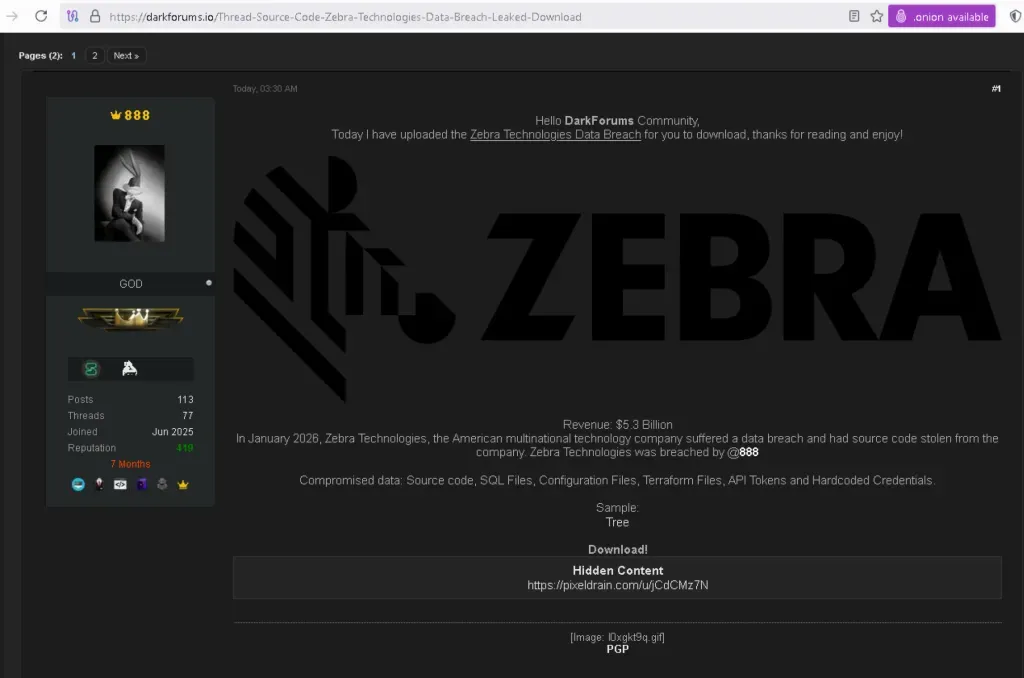
In January 2026, Zebra Technologies — the U.S.‑based multinational technology company with approximately $5.3 billion in annual revenue — experienced a significant data breach. A threat actor operating under the alias @888 claimed responsibility for the incident, alleging that they accessed and exfiltrated sensitive internal assets from the company’s systems.
Compromised Data
According to claims from the threat actor, the breach resulted in the theft of:
- Source code repositories
- SQL database files
- Configuration files
- Terraform infrastructure files
- API tokens and hardcoded credentials
This type of data, if legitimate, could pose operational, security and intellectual property risks for Zebra Technologies and its partners.
Where Was the Data Found?
The stolen materials are reportedly circulating on underground forums or marketplaces where threat actors share or sell compromised corporate data. Such platforms are frequently monitored by cybersecurity analysts tracking breach activity.
Company Data Breach History
As of now, there have been no widely reported or confirmed public disclosures by Zebra Technologies about this specific January 2026 breach in mainstream cybersecurity news sources or official company statements. Public reporting on data breaches often lags behind threat actor claims, particularly when initial information comes from underground postings.
Impact and Risks
If the breach and the types of stolen files are accurate:
- Intellectual property theft: Source code and configuration files could reveal proprietary logic and infrastructure design.
- Security exposure: Hardcoded credentials and API tokens can provide attackers with persistent access or entry points into enterprise systems.
- Operational risk: Leaked Terraform and SQL files can expose environment configurations and database schemas, potentially facilitating further attacks.
- Reputational harm: Public knowledge of internal data compromise may affect customer and partner trust.
Recommendations for Users & Organizations
For companies and individuals monitoring digital safety:
- Investigate and verify: Zebra Technologies and its IT/security teams should conduct a forensic investigation to confirm the scope of any breach.
- Rotate credentials: Immediately revoke and replace exposed credentials, API tokens, and keys.
- Review access controls: Implement stricter credential management policies and avoid hardcoding secrets in code.
- Increase monitoring: Deploy security monitoring on critical systems to detect unauthorized activity.
- Engage specialists: Consider external cybersecurity expertise to assist with remediation and incident response.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.