Data Breach News2 min read
Stellium Data Breach: 360GB Database Claimed by Everest
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Overview
In February 2026, the ransomware group Everest claimed responsibility for a cyberattack targeting Stellium (stellium.com), a consulting firm specializing in supply chain and SAP-based business optimization services.
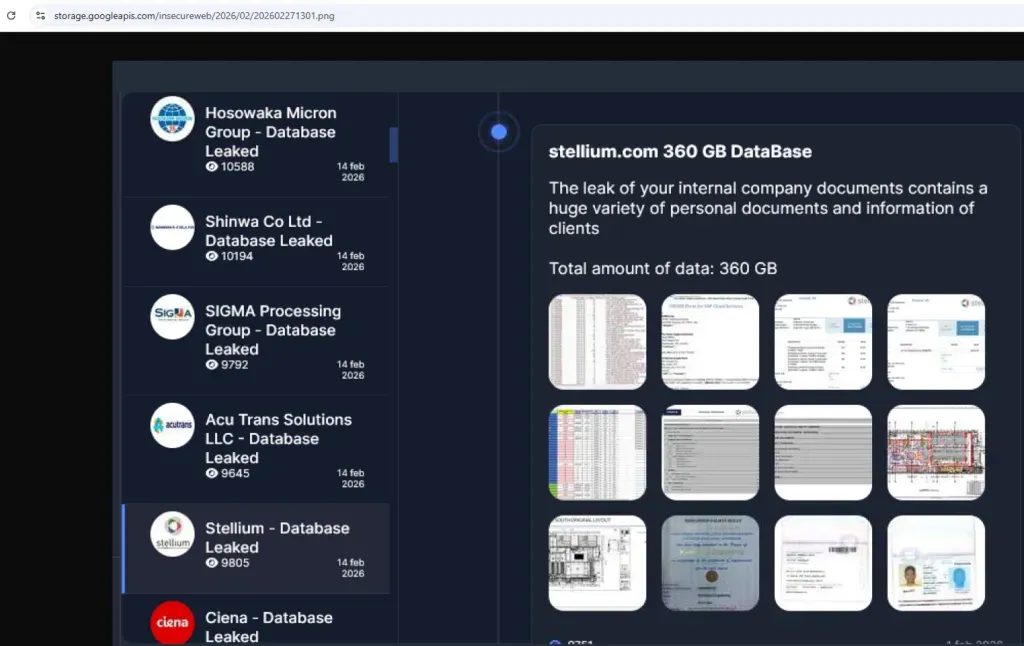
According to the leak announcement, attackers allegedly exfiltrated approximately 360 GB of internal company data, which reportedly includes sensitive corporate documents and personal information related to clients and internal operations.
The threat actors indicated that the data may be released publicly if negotiations with the company are not initiated.
Where Was the Data Found?
The dataset was reportedly advertised on a ransomware leak site operated by the Everest group, a threat actor known for publishing stolen corporate data to pressure victims into paying a ransom.
Screenshots shared with the leak claim show a large collection of internal files and documents, including:
- Client and personal documents
- Internal spreadsheets and databases
- Financial and operational records
- Project documentation and consulting materials
- Identity documents and sensitive internal files
The exposed archive is estimated to be around 360 GB in size, suggesting a significant amount of corporate and potentially client-related information.
Company Data Breach History
Public reports indicate that Stellium was listed as a victim of the Everest ransomware group on February 1, 2026, marking the first widely reported cybersecurity incident involving the company.
At the time of writing, there are no confirmed earlier major public breaches associated with Stellium.
Impact and Risks
If the leaked dataset is authentic, several risks could emerge for both the company and its clients:
- Identity theft and fraud: Personal documents could be used for impersonation or financial fraud.
- Phishing and business email compromise (BEC): Attackers may craft highly convincing phishing campaigns using real internal data.
- Corporate espionage: Confidential consulting strategies or supply chain data could be valuable to competitors.
- Credential abuse: Any exposed login credentials could lead to unauthorized access to internal or cloud systems.
Consulting firms are particularly sensitive targets because they often store strategic and operational data belonging to multiple enterprise clients, which could increase the impact of such a breach.
Recommendations for Users
If you have interacted with Stellium or shared data with the company, consider taking the following precautions:
- Change passwords immediately, especially if reused across services
- Enable two-factor authentication (2FA) wherever possible
- Monitor financial accounts and emails for suspicious activity
- Be cautious of phishing emails that reference projects, invoices, or internal communications
- Use unique passwords for each service and consider a password manager
Organizations that worked with the firm should also review access permissions and rotate any shared credentials or API keys.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.