Data Breach News2 min read
Magento Breach via Third‑Party: 261K Phones & 430K Emails
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
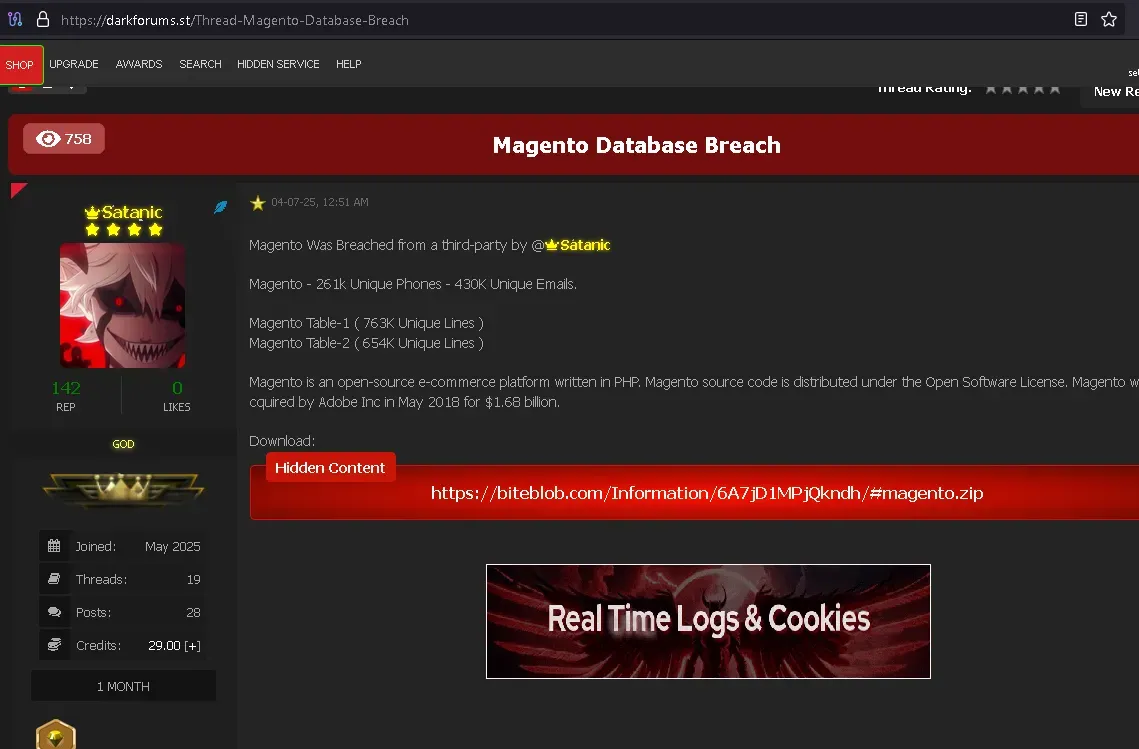
In April 2025, threat actor @Satanic reportedly compromised Magento—via a third-party integration—exposing sensitive CRM data on darkforums.st. The leaked dataset includes:
-
261,000 unique phone numbers
-
430,000 unique email addresses
-
Two tables:
- Table‑1: 763,000 unique lines
- Table‑2: 654,000 unique lines
Magento is an open-source e‑commerce platform written in PHP, acquired by Adobe Inc. in May 2018 for $1.68 billion
Where and How?
The breach was claimed by @Satanic on darkforums.st, targeting a third-party CRM integrated with Magento platforms. Researchers analyzed the dump, confirming the inclusion of emails, phone numbers, company info, and other identifiers linked to over 700,000 records overall
Context: Magento Supply‑Chain Risks
This incident aligns with a broader trend of supply-chain attacks affecting Magento:
- A wave of malicious backdoors in 21 Magento extensions (from vendors like Tigren, Meetanshi, and Magesolution) was activated in April 2025, compromising 500–1,000 stores, including high-profile brands, through PHP backdoors hidden since 2019
Company Data Breach History
There have been no earlier CRM data breaches publicly linked to Magento itself via third-party integrations. However:
- The April 2025 supply-chain attack highlights systemic risks in the Magento ecosystem
- Parent company Adobe has not confirmed this breach
Further Action
- Checksum & schema capture – save details on both tables to avoid repost detection.
- Dark web monitoring – track platforms like darkforums.st and BreachForums for further dumps or sales.
- Notify impacted businesses – Magento shop owners should audit CRM integrations, rotate credentials, and reinforce supply-chain security.
- Enhance platform defenses – encourage scanning for malicious extensions, cleaning infected stores, and isolating compromised components.
Recommendations for Affected Organizations
✅ Perform immediate full-stack audit of CRM and third-party plug-ins
✅ Rotate all API tokens, credentials, and encryption keys
✅ Remove or update compromised extensions and validate code integrity
✅ Monitor server logs for unauthorized access or unusual behavior
✅ Implement zero-trust architecture and continuous code-level monitoring
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.