Data Breach News2 min read
Git Repository Misconfiguration Exposes VocesCredicorp Data
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
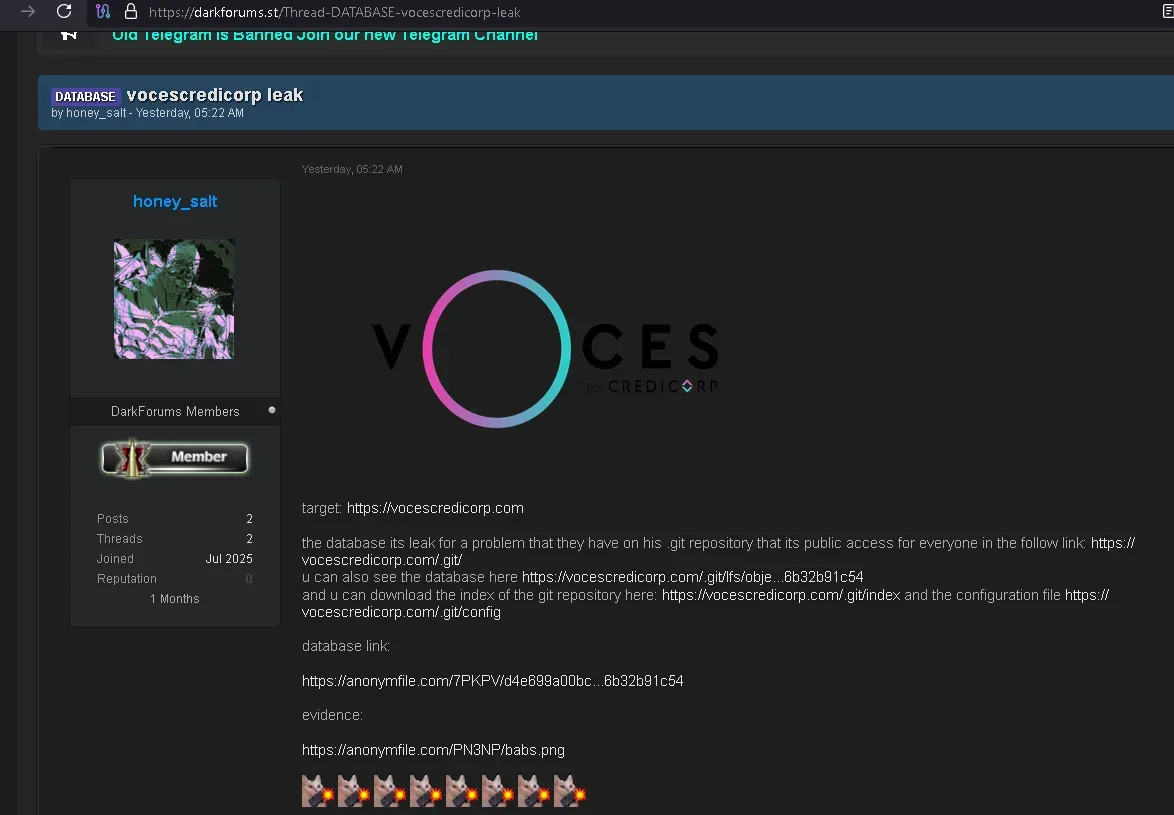
A critical security misconfiguration has led to the exposure of sensitive data from the website vocescredicorp.com. On August, 2025, it was discovered that the .git directory of the domain was publicly accessible, potentially allowing unauthorized access to configuration files, codebase history, and sensitive data. The incident was reported by the dark web user honey_salt on the forum darkforums.st, raising concerns about the organization’s development environment security.
The exposure includes access to files such as the Git index, configuration file, and Git LFS objects. These files can be used to reconstruct the entire source code repository, extract credentials, and analyze the structure of internal systems.
Where and How?
The misconfiguration was found on the live production domain of VocesCredicorp:
.git/directory: https://vocescredicorp.com/.git/- Git index: https://vocescredicorp.com/.git/index
- Configuration file: https://vocescredicorp.com/.git/config
- Git LFS objects: https://vocescredicorp.com/.git/lfs/objects/
The publicly accessible .git directory allows full download of the repository, exposing not only the source code but potentially sensitive credentials or API keys embedded in commit history. This kind of exposure is commonly exploited by attackers to infiltrate systems or gain further access to infrastructure.
Company Data Breach History
There are no previously reported data breaches involving VocesCredicorp. However, the exposure of the .git repository highlights significant gaps in basic server hardening and version control hygiene. Without swift remediation, this incident could lead to further compromise of internal systems or customer data.
Further Action
The affected organization should immediately:
- Restrict public access to the
.gitdirectory - Conduct a full audit of exposed content
- Revoke and rotate any potentially compromised credentials
- Notify users if any sensitive information was exposed
- Implement stricter deployment and security validation pipelines
Recommendations for Personal Data Protection
While this breach appears to be related to infrastructure and code exposure, users should always remain cautious:
- Avoid using the same password across multiple platforms
- Enable two-factor authentication where possible
- Be alert for phishing emails pretending to be from official sources
- Monitor accounts for suspicious login attempts or activity
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.