Data Breach News2 min read
Employee Data from PT IBS Leaked Online (232K+ Rows)
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
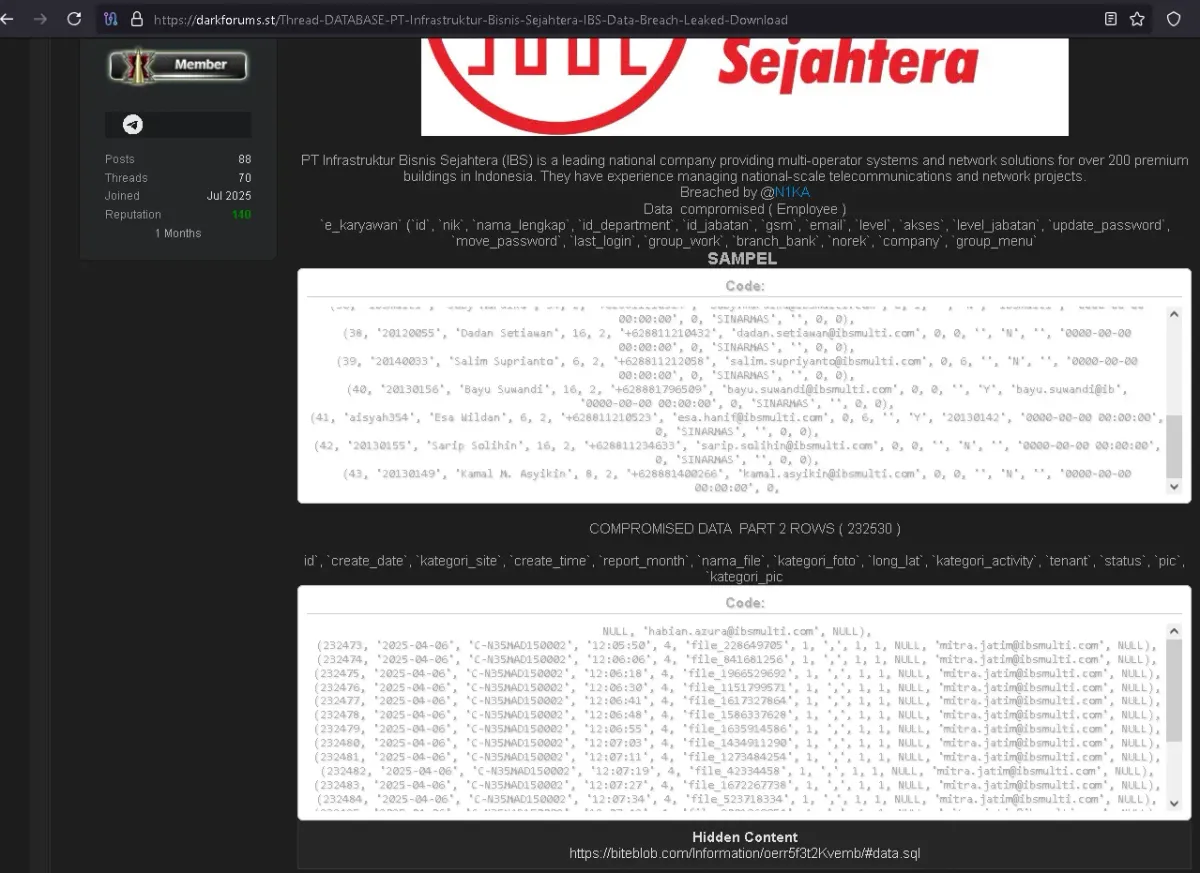
A new data breach targeting PT Infrastruktur Bisnis Sejahtera (IBS) has surfaced, exposing sensitive employee and operational records. The dump was published on darkforums.st by the user @N1KA in August 2025.
IBS is a major Indonesian provider of multi-operator network systems and telecommunications infrastructure, with services in over 200 premium buildings nationwide. The company is known for managing large-scale telecom projects across Indonesia.
What Was Leaked?
The exposed data appears to include:
-
Full employee information from the
e_karyawantable, including:- Employee IDs (NIK), full names, phone numbers, corporate emails
- Job titles (e.g., COO, CFO, Head of Planning)
- Department and position details
- Password fields, login history, bank account numbers (linked to SINARMAS)
- Access levels and internal group assignments
-
A second dataset with over 232,000+ rows tied to:
- Site and activity logs
- File names, timestamps, tenant metadata
- Involvement of third-party emails such as
mitra.jatim@ibsmulti.comand others
This leak contains potentially exploitable credentials and internal operational metadata.
Company Data Breach History
At the time of this post, there are no previously reported data breaches involving PT IBS. However, the company has been mentioned in national headlines due to legal investigations tied to the BTS corruption case in Indonesia. These involve executives being questioned over public infrastructure contracts, but no prior cybersecurity incidents have been made public.
Further Action
Given the nature of the leaked employee records, PT IBS should:
- Investigate potential entry points and system vulnerabilities.
- Notify impacted employees, especially those with exposed personal and financial details.
- Improve internal access controls and data encryption.
- Issue a formal breach disclosure and engage local data protection authorities.
Recommendations for Personal Data Protection
If affected by this breach, employees and stakeholders should:
- Immediately change work-related passwords and any reused credentials.
- Watch for phishing attempts via SMS or email.
- Monitor bank accounts and mobile services linked to leaked phone numbers.
- Enable 2FA across all accounts.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.