Data Breach News2 min read
787MB of Sensitive Data Leaked from Logs_23 April Database
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
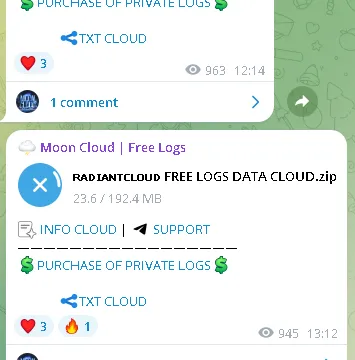
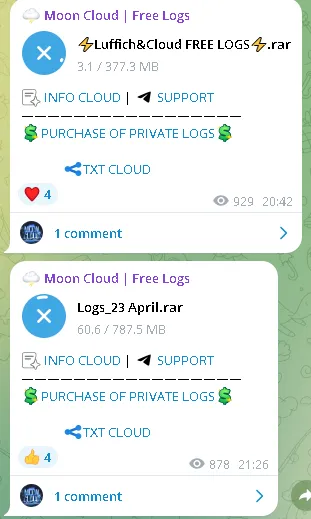
InsecureWeb has uncovered a new data breach involving the Logs_23 April database, which was detected in April 2024. Leaked by the hacker group #mooncloud, the breach exposed 787MB of sensitive data, including email addresses, via combolists. The breach was detected on Telegram, where compromised data is frequently traded. This marks yet another leak from the Logs_23 April database, raising concerns about the platform’s continued security vulnerabilities. InsecureWeb detected this breach during its regular dark web scanning operations.
Where and How?
The breach occurred on Telegram, where a combolist from Logs_23 April containing 787MB of email addresses was exposed. This leak follows a pattern of recurring incidents involving this particular database, suggesting a failure to secure personal information effectively. A “combolist” typically includes a large collection of credentials, often harvested from various data breaches, which are then sold or shared for malicious purposes. The fact that this data was found on chat apps like Telegram, a notorious hotspot for cybercriminal activity, emphasizes the need for heightened security measures within the victim’s infrastructure.
Company Data Breach History
The Logs_23 April database has faced multiple security breaches in the past, pointing to recurring vulnerabilities in its systems. Previous leaks have included sensitive data like emails, which hackers have exploited repeatedly. Despite these incidents, it seems that significant security improvements have yet to be implemented, leaving users’ data at continued risk. Without prompt and robust action, Logs_23 April could face further breaches, further compromising its users’ personal information.
Further Action:
InsecureWeb encourages the breach victim to investigate the source of the breach, implement stronger security measures, and communicate transparently with its users about the incident and the measures taken to mitigate the risks.
Recommendations for Personal Data Protection
How Users Can Protect Their Information
To protect their personal information and accounts from being compromised, users should take the following steps:
– Change their passwords frequently, with a combination of letters, numbers, and symbols.
– Enable two-factor authentication whenever possible.
– Use unique passwords for each account, to prevent hackers from accessing multiple accounts with the same password.
– Be cautious of suspicious emails or messages, as they may contain phishing links that can compromise their accounts.
– Regularly monitor their accounts for any suspicious activity.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.