Data Breach News2 min read
171K Foodco.us Credentials Shared on LeakBase
By InsecureWeb Team
This report reflects observations of dark web activity. InsecureWeb makes no representations regarding the accuracy of this data.
Data Breach Summary
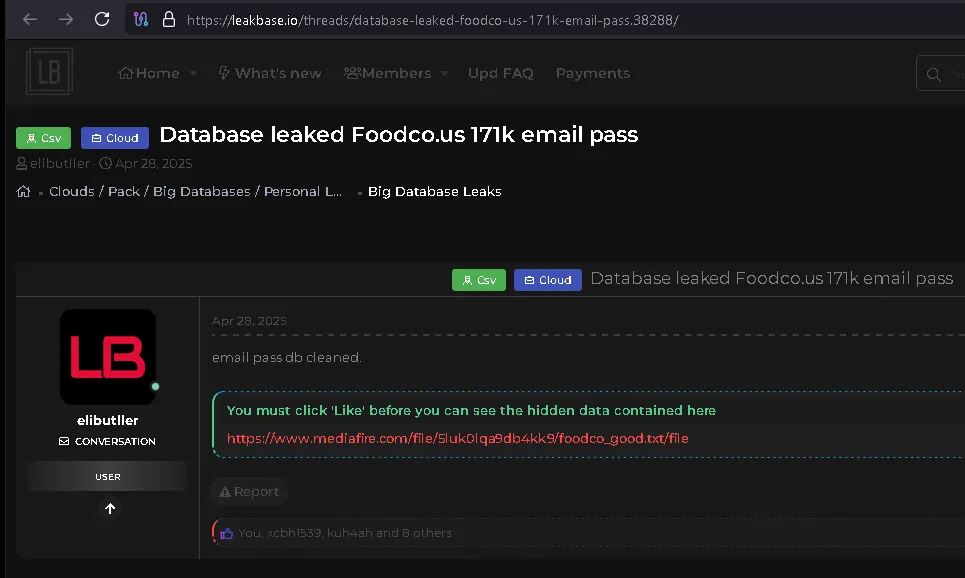
On April 28, 2025, a data breach involving the website Foodco.us was identified on the underground forum LeakBase.io. A user named elibutler publicly shared a cleaned credential database containing approximately 171,000 email and password combinations. The dataset was made accessible through an external link hosted on MediaFire, allowing unrestricted downloads by other forum members after minimal interaction.
Where and How?
The breach was posted in the “Big Database Leaks” section of LeakBase, a forum commonly used by threat actors to distribute and trade stolen data. The post included a MediaFire link to a plain text file labeled foodco_good.txt, which presumably contains valid email:password pairs. While the database was referred to as “cleaned,” there’s no indication of hashing or encryption, suggesting the credentials may be in plaintext or easily decodable formats.
The nature of the leak points to a previously compromised system or poor security hygiene on the part of Foodco.us, where credentials may have been stored insecurely or obtained via phishing, malware, or credential stuffing.
Company’s Data Breach History
A search of publicly available sources reveals no officially reported breaches of Foodco.us in 2023, 2024, or 2025. However, the appearance of this credential dump strongly suggests the website or one of its related services may have suffered a stealth or unreported breach. No breach notifications appear on their official website or major cybersecurity reporting platforms.
This incident raises concerns about the company’s data security practices and whether users have been informed about this exposure.
Further Action
Foodco.us should:
- Immediately investigate the origin of the leaked data.
- Notify affected users and reset all potentially compromised credentials.
- Conduct a full security audit, including application, database, and access logs.
- Implement stronger password hashing, rate-limiting, and multi-factor authentication.
- Report the incident to the appropriate regulatory authorities, if applicable.
Recommendations for Personal Data Protection
How Users Can Protect Their Information
To safeguard personal information and accounts, users should consider the following steps:
- Change Passwords Regularly: Use strong, unique passwords combining letters, numbers, and symbols.
- Enable Two-Factor Authentication (2FA): Whenever possible, activate 2FA to add an extra layer of security to accounts.
- Use Unique Passwords for Each Account: Avoid reusing passwords across different platforms to prevent multiple account compromises.
- Be Cautious of Phishing Attempts: Stay vigilant against suspicious emails or messages that may contain malicious links or solicit personal information.
- Monitor Accounts for Unusual Activity: Regularly review account statements and activities to detect and respond promptly to unauthorized actions.
By adopting these practices, users can enhance their personal data security and reduce the risk of unauthorized access to their information.
What is InsecureWeb?
InsecureWeb is a Dark Web monitoring service that keeps track of recent data breaches and tracks their impact by monitoring the darkest places of the internet.
Our commitment lies in providing top-notch cybersecurity services to our clients. Through continuous monitoring of the dark web and advanced threat detection methodologies, we strive to identify potential breaches promptly, enabling swift response and mitigation efforts. With our state-of-the-art tools and expertise, we prioritize the confidentiality, integrity, and availability of our clients’ data.